Showing posts with label HACKING TRICKS. Show all posts

Monday, June 25, 2012

Top 10 Most Infamous Black Hat Hackers of All Time

In the world of information technology, black hat hackers (also known as crackers or cyber-criminals) are known as the bad guys or villains. Most of them break into computers or networks without authorization to steal Money and classified and sensitive information, while others are doing it simply for the challenge or the thrill of hacking. To accomplish their sinister work, crackers often create malware (malicious software) like viruses and worms to gain control of computer systems.


I have gathered here a list of ten of the most popular cyber-criminals the world has ever known. These evil geniuses were involved in high profile hacking that possibly caused millions, if not billions of dollars in total damages. However, some of them have now turned to the good side and are using their talents for the benefit of mankind.


Without further delay, here are the top 10 most infamous black hat hackers of all time:


10. Jonathan James
At the age of 16, Jonathan James (also known as c0mrade) became the first juvenile imprisoned for cybercrime in the United States. James carried out a series of intrusions into various systems including the computers of the Defense Threat Reduction Agency (DTRA) of the US Department of Defense. James had installed an unauthorized backdoor in a computer server in Dulles, Virginia that he used to install a sniffer allowing him to intercept over three thousand messages passing to and from DTRA employees while collecting countless usernames and passwords. This intrusion caused NASA to shut down its computers for three weeks costing them $41,000 to check and secure their systems. Jonathan James committed suicide in 2008.


9. Kevin Poulsen
Kevin Poulsen (also known as Dark Dante) is a notorious black hat hacker in the 1980s. One of his popular hacks was a takeover of all of the telephone lines for Los Angeles radio station KIIS-FM, assuring that he would be the 102nd caller, and the likely winner of a brand new Porsche 944. Poulsen went underground as a fugitive when the FBI started pursuing him, but was finally captured in 1991. He pleaded guilty to seven counts of mail, wire and computer fraud, money laundering, obstruction of justice, and for obtaining information on covert businesses run by the FBI. Kevin Poulsen was sentenced to 51 months in prison, which at that time was the longest sentence ever given for cracking. He is now a free man and is a senior editor at Wired News.


8. Albert Gonzalez
Albert Gonzalez is a cyber-criminal accused of masterminding the biggest ATM and Credit Card theft in history. From 2005 through 2007, he and his group have allegedly sold more than 170 million card and ATM numbers. Gonzalez's team used SQL injection techniques to create malware backdoors on several corporate systems in order to launch packet-sniffing (specifically, ARP Spoofing) attacks, which allowed him to steal computer data from internal corporate networks. When he was arrested, authorities seized $1.6 million in cash including $1.1 million in plastic bags placed in a three-foot drum buried in his parents' backyard. Earlier this year, Gonzalez was sentenced to 20 years in federal prison.


7. Michael Calce 
In February 2000, Michael Calce (a.k.a. MafiaBoy) launched a series of highly publicized denial-of-service attacks against large commercial websites. His victims include Yahoo!, Amazon.com, Dell, eBay, and CNN. He hacked Yahoo! when it was still the web's leading search engine causing it to shutdown for about an hour. Calce exploited websites primarily for pride and to establish dominance for himself and his cybergroup named TNT. In 2001, the Montreal Youth Court sentenced him to eight months of open custody, one year of probation, restricted use of the Internet, and a small fine.


6. Markus Hess
Markus Hess is a German hacker in the late 1980s that was recruited by the KGB and was involved in a Cold War computer espionage incident. All the way from Germany, he was able to access computer systems from the Lawrence Berkeley Laboratory (LBL) located in California. By using LBL to “piggyback” to ARPANET and MILNET, Hess attack 400 U.S. military computers including OPTIMIS Database (The Pentagon), Anniston Army Depot, U.S. Air Force (Ramstein Air Base, West Germany), Fort Buckner, Camp Foster (Okinawa, Japan). He went to trial in 1990 and was found guilty of espionage. Hess was sentenced to a one to three year prison sentence but was eventually released on probation.


5. Vladimir Levin
Vladimir Levin is known for his involvement in the attempt to illegally transfer 10.7 million US dollars via Citibank's computers. In 1997, Levin was brought into U.S. custody, and he admitted to only one count of conspiracy to defraud and to stealing $3.7 million. The following year, he was convicted and sentenced to three years in prison, and ordered to pay more than $200,000. Of the stolen $10.7 million, Citibank claimed that only around $400,000 had been recovered. At the moment, Levin is free and now lives in Lithuania.


4. Robert Tappan Morris
Robert Tappan Morris is an 'accidental' black hat hacker infamous for creating the first ever computer worm on the Internet known as Morris Worm. In 1988, he created the worm while he was a graduate student at Cornell University with the original aim of measuring the size of the Internet or counting the number of computers connected to it. The Morris Worm spread rapidly and infected thousands of computers. The cost of possible loss in productivity caused by the worm at each system ranged from $20,000 to more than $530,000 as estimated. Without serving jail time, Morris was sentenced to community service, probation, and a fine of $10,000. He is currently a professor at Massachusetts Institute of Technology (MIT), in the Institute's department of Electrical Engineering and Computer Science.


3. Adrian Lamo
Adrian Lamo is widely known for breaking into a series of high-profile computer networks that include The New York Times, Microsoft, Yahoo!, and MCI WorldCom. In 2002, he added his name to the The New York Times' internal database of expert sources and used LexisNexis account to conduct research on high-profile subjects. The Times filed a complaint, and a warrant for Lamo's arrest was issued, followed by a 15-month investigation by federal prosecutors in New York. After several days in hiding, he surrendered to the US Marshals, and then to the FBI. Lamo was ordered to pay around $65,000 in damages and was sentenced to six months house arrest at his parents' home, plus two years probation. In June 2010, Lamo disclosed the name of Bradley Manning to U.S. Army authorities as the source of the July 12, 2007 Baghdad airstrike video leak to Wikileaks. At present, he is working as a threat analyst and donates his time and skills to a Sacramento-based nonprofit organization.


2. Gary McKinnon
Gary McKinnon has been accused of what one US prosecutor claims is the "biggest military computer hack of all time". Between February 2001 and March 2002, he reportedly exploited 97 United States military, Department of Defense, and NASA computers. McKinnon allegedly deleted critical files from operating systems that shut down the US Army’s Military District of Washington network of 2,000 computers for 24 hours. He supposedly deleted US Navy Weapons logs, causing a naval base's network of 300 computers unusable after the September 11th terrorist attacks. McKinnon is also charged with copying of sensitive data, account files, and passwords onto his own computer. He expresses that he was only looking for evidence of free energy suppression, a cover-up of UFO activity, and other technologies that may be useful to the public. At present, McKinnon is awaiting extradition to the United States.


1. Kevin Mitnick 
Kevin Mitnick was once considered as the most wanted computer criminal in United States history. He was involved in a highly publicized pursuit by authorities that his misadventures were depicted in two hacker films: Takedown (a.k.a. Hackers 2) and Freedom Downtime. While he was a fugitive, he cracked dozens of computer networks and copied valuable proprietary software and stole corporate secrets from some of the largest cellular telephone and computer companies in the US. Mitnick also intercepted and stole computer passwords, altered computer networks, read private e-mails, and cloned cellular phones to hide his location. In 1999, he confessed to four counts of wire fraud, two counts of computer fraud and one count of illegally intercepting a wire communication. Mitnick was sentenced to a total of 68 months in prison and was incarcerated for 5 years that included 8 months in solitary confinement. He was released in 2000 and is now a well-known computer security consultant, public speaker, and author.

10 Best Hacker Movies (Films about Computer Hacking) of All Time


As a certified geek, it is always pleasing to see movies that involve Computer Hacking or hackers in action. Although most of these films don't always represent the real deal, some of them have what it takes to excite, amuse, and inspire those who are passionate about computers.

I have here my top 10 list or my all time favorite hacker movies or films that involvecomputer hacking. Feel free to share yours on the comment section later on:

10. Swordfish
If you are a big fan of Halle Berry and of course, computers, then this movie is for you. This action-packed film involves a high-tech robber/villain named Gabriel Shear (John Travolta) against Stanley Jobson (Hugh Jackman), a super hacker convicted by the FBI but who is trying to stay clean. Gabriel is the leader of a covert counter-terrorist unit called Black Cell who wants to steal $9.5 billion worth of Money  from a secret government slush fund (codenamed Swordfish). But since it's locked up behind a complicated encryption system, he offers the desperate Stanley $10 million to hack into the system and steal themoney for him.


9. Track Down (aka Hackers 2)
Track Down, also known as Takedown or Hackers 2, is a film based on the book written by computer security expert Tsutomu Shimomura and journalist John Markoff, which tells the story of how they tracked down and helped the FBI arrest the most notorious computer hacker in the US -Kevin Mitnick. For several years, Mitnick had evaded Federal agents while breaking into numerous computers and gain access to sensitive and valuable information. When he hacked the system of Shimomura, it began a daring chase through cyberspace between two computer geniuses working on different sides of the law.


8. Antitrust
Antitrust is a fictional story of two idealistic computer whiz kids who are best friends. After graduating from Stanford, Milo and Teddy are offered jobs at NURV, a giant Portland company headed by CEO Gary Winston, and is on the brink of completing a global communication system. Milo accepts the job while Teddy declined and continues to work on a media compression program he wants to release for free. Winston takes a personal interest in Milo, whose genius can help NURV meet its launch date, and Milo responds with intelligence and hard work. But when Teddy meets with tragedy, Winston's irrational remark makes Milo suspicious. So he decides to investigate Winston and his company.


7. Sneakers
Sneakers is a star-studded film that tells the story of Martin Bishop (Robert Redford), head of a group of experts who specialize in testing security systems. When he is bribed by Government agents into stealing a top secret black box, the team find themselves involved in a game of danger and conspiracy. After getting the box, they discover that it has the capability to decode every existing encryption system around the world. The problem is that the agents who hired them didn't work for the Government after all.


6. Die Hard 4: Live Free or Die Hard
The fourth instalment in the Die Hard series is geeky enough for me to be included on this list. The story revolves around a group of super hackers/cyber terrorists who plan to hack FBI computers and takes over several U.S. technology infrastructures. Thanks to Bruce Willis' immortality and the aid of non-evil computer geeks headed by Justin Long (aka The Mac Guy), the movie has a happy ending.


5. The Net
Angela Bennett (Sandra Bullock) is a young and beautiful computer expert who becomes involved in a web of computer espionage. Only hours before she leaves for vacation, she discovers secret information on the disk she has received from a friend that turns her life into a living nightmare. Her records are erased from existence and she is given a new identity so she struggles to find out why this has happened to her.


4. Hackers
I think this movie is really popular among geeks for two reasons: Angelina Jolie and well, it is a story about hackers. The film follows the adventures of a group of gifted high school hackers and their involvement in a corporate extortion conspiracy. The lead character, Dade "Zero Cool" Murphy (Jonny Lee Miller), is arrested by the US Secret Service for writing a computer virus, banning him from using a computer until he turns 18. Years later, he and his hacker friends discover a plot to unleash a dangerous computer virus allowing them to use their computer skills to find the evil computer genius behind the virus while being pursued by the Secret Service.


3. Tron
Tron is an action-filled science fiction film that tells the story of a hacker who is literally abducted into the world of computer and forced to participate in gladiatorial games where his only chance of escape is the help of a heroic security program. The movie has been described by a film critic as "a technological sound-and-light show that is sensational and brainy, stylish, and fun".


2. The Matrix (Trilogy)
An all time list of movies about hacking is never complete without including The Matrix. Its trilogy is a mainstream success, so I presume that you have seen at least one instalment or know something about The Matrix. But for those of you who are clueless, the film tells the story about a computer hacker known as Neo (Keanu Reeves) who learns from mysterious underground hackers about the real nature of his existence and his main role in the war against the controllers of it.


1. WarGames
WarGames is a film about a young hacker who unknowingly gains access to WOPR, a United States military supercomputer programmed to predict possible after-effects of nuclear war. He gets WOPR to run a nuclear war simulation, initially perceiving it to be a computer game, which caused a national nuclear missile scare and nearly initiates World War III.


If you would like to share your favorite movies about hackers or hacking, please do so via comment.

Saturday, November 26, 2011

BMP Thumbnail As Icon


You can actually change the default BMP icon to a thumbnail version of the actual BMP file. To do this simply go to:


HKCU\Paint.Picture\Default.

In the right pane change the value of default to %1.


To restore back to the normal change the vale of default back to: C:\Progra~1\Access~1\MSPAINT.EXE,1.

Please note however that this will slow down the display rate in explorer if there are too many BMP thumbnails to display. You can use other icons too, simply enter the pathname.

Customize the Shortcut Arrow


All shortcuts have a tiny black arrow attached to it's icon to distinguish from normal files. This arrow can sometimes be pretty annoying and as a Hacker should know how to change each and everything, here goes another trick. Launch the Registry Editor and go to:


HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\explorer\Shell Icons.


Now, on the right pane is a list of icons ( we found out that on some systems, Windows 98 especially, the right pane is blank. Don't worry, just add the value as required ). Find the value 29. If it isn't there, just add it. The value of this string should be

C:\Windows\system\shell32.dll, 29

( which means the 30th icon in shell32.dll - the first one begins with 0 ).

Now, we need blank icon to do this. Just create one with white as the whole icon. Go here to learn how to create an icon. Once done just change the value to C:\xxx.ico, 0 where "xxx" is the full path of the icon file and "0" is the icon in it.


Now for some fun. If the blank icon is a bit boring, change it again. You will find that under shell32.dll there is a gear icon, a shared folder ( the hand ) and much more. Experiment for yourself!

Making the Internet Explorer & the Explorer Toolbars Fancy


The Internet Explorer toolbar looks pretty simple. Want to make it fancy and kewl? Why not add a background image to it. To do this kewl hack launch the Windows Registry Editor and go to the following key:

HKEY_CURRENT_USER\SOFTWARE\Microsoft\ Internet Explorer\Toolbar\


Now in the right pane create a new String Value and name it BackBitmap and modify it's value to the path of the Bitmap you want to dress it up with by rightclicking on it and choosing Modify.

When you reboot the Internet Explorer and the Windows Explorer toolbars will have a new look.

Change Internet Explorer's Caption

Don't like the caption of Internet Explorer caption? Want to change it? Open the registry editor and go to


HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Internet Explorer\Main

In the right pane create a new String Value names Window Title (Note the space between Window and Title). Right click on this newly created String Value and select Modify. Type in the new caption you want to be displayed. Restart for the settings to take place.

Outlook Express Tricks


Colorful Background
Don't like the boring background colors of Outlook Express? To change it launch the Windows Registry Editor and scroll down to the

HKEY_CURRENT_USER\Software\Microsoft\Internet Mail And News key.

On the left pane, click on ColorCycle or select Edit and Modify in the menu. Now change the value to 1. Close and restart. Now, launch Outlook Express and whenever you open up a New Message, hold down ctrl-shift and tap the z key to scroll to change the background color. Repeat the keystroke to cycle through the colors.

Internet Explorer 5 Hidden Features


Microsoft Internet Explorer 5 has several hidden features which can be controlled using the Windows Registry. Open your registry and scroll down to the following key:


HKEY_CURRENT_USER\Software\Policies\Microsoft\Internet Explorer\Restrictions

Create a new DWORD value named x(See complete list of values of x below) and modify it's value to 1 to enable it and to 0 to disable it.

Disable 8.3 Name Creation in NTFS


Files that use the 8.3 naming convention can degrade NTFS drive performance.

Unless you have a good reason for keeping the 8.3 naming convention intact (such as if you’re using 16-bit programs), a performance gain can be achieved by disabling it.

Set the Registry

DWORD key HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\FileSystem\NtfsDisable8dot3NameCreation to 1.

Exit the Registry and reboot.

Hack a Forum using XSS


To defaced or even attempt to hack a forum. The forum must have HTML enabled, so you can

enter some malicious codes. If the forum does have HTML enabled then you can enter codes such as;


Code:


If the forum allows the imagen tags then you can use this tag to

steal peoples cookies.

Code:


Enjoy!!!!!!!!!!!!!!!!!!!

Cable Modem IP Hijacking in Win95/98


The purpose of this is to show you how bad cable modems security is and that even with a win box you can take someone else's IP. You can hijack IP's using a cable modem and it's very simple in any operating system. Just follow the steps:


1) Choose someone's IP that you wish to have. Make sure the IP is on the same network. Most cable modem providers use DHCP. The fist thing you have to do is find the victims IP. Remember the victims IP has to be in the same network and with the same service provider for this to work.


2) Now this is probably the hardest thing in this file (but it's still easy), you have to wait until the victims computer is off or you can Smurf kill his connection. When you think his computer is off-line just try to ping

it to see if you get a response. Do this by going to a DOS prompt and typing "ping ". If you get a response then you have to try harder.


After you get his PC off-line then you go into your network properties and edit the IP settings, but instead of having yours there you put the victims IP, host, and domain.


3) Restart. If you restart and you get an IP conflict this means that the victims computer is on, if you don't get an IP conflict then try to go to your web browser and see if it works. With some cable modem providers you


might have to also add the Gateway, Subnet mask (255.255.55.0), Host, DNS search, and Domain.


Now you can go. Everything will work until the victims PC is back on. Once it is back online it will take the IP away because it will tell you that you have the wrong Mac addresses.


*Linux*

This is also possible in Linux, but is not the best way. You can change your Mac address to the victims PC and this is more secure and much easier. There are a couple of scripts to change your address, just look around.

Warning: Some cable modem service providers will know when you're using the wrong IP, but hey, it might be useful.

Wednesday, October 5, 2011

14. Myspace Hack: How to Hack Myspace Account Passwords


Have you ever seen your friend post a bulletin on MySpace about how they made a $1,000 on the weekend? It’s the first sign your friend’s MySpace account has been hacked. Maybe you’ve had your MySpace account hacked and would like to know what you can do to prevent it from happening again in the future. Then this post is for you.
Phishing: Most people have their account hacked by clicking on a stranger’s profile only to be taken to what looks like the MySpace login screen. Turns out it’s not a MySpace login screen and the username and password you just entered is saved for future use by the bad guys(hackers). The biggest thing is if you find yourself suddenly sent to the login page when you haven’t signed out, look at the url and make sure it says myspace.com in the address bar. If it has happened to you, you should be able to remedy the problem by simply changing your password watching for the proper web address in the future.
For more on Phishing and the method used for hacking Myspace account by Phishing refer:
Hack email accounts by Phishing.
Viruses: Another way people have their account hacked is from malware installed on their system that records their keystrokes. This is an uncommon problem for MySpace accounts because people looking to watch your keystrokes wouldn’t risk the legal trouble for MySpace accounts. They’d much rather take your bank account or something more valuable. If you change your password repeated times and you keep getting hacked, then you may have a virus and you’ll need to reinstall your operating system and start over.
Spy Software: Keylogging is the best and most guaranteed way to obtain a myspace password because not only can their myspace password, but you can get the passwords to everything they have and see every piece of information entered on the computer. Keylogging refers to the monitoring of key’s pressed on a keyboard, but most spy software contain many more usefull features. Some software does not even require you to touch the person’s computer, which many people find extremely usefull. I have tried many many different software solutions, and here is what I recommend.
If you have physical access to their computer, this should be relatively easy. For this situation, we recommend a keylogging software such as Ardamax keylogger . You can simply install it on the computer that they use and it will log all activity on the computer, including capturing the MySpace password. I recommend Ardamax keylogger because it has a unique MySpace capture feature that saves a screenshot of every page visited on the site and also has a great interface.
If there’s no way you can physically access their computer, it can be a little trickier to pull off. The program i’ve found that works the best (and gets so close to this ethical line) is a service called SniperSpy. SniperSpy gives you a module that you can send to your target that will allow you to spy on their computer’s every action. No physical access to the target’s computer is needed. You can view their computer screen LIVE from anywhere at anytime via your web browser, which means you don’t need to install anything on your computer either. You will be able to look at chat conversations, web sites visited, and gain access to all the online accounts they log into while being SniperSpyed. It even takes image screenshots of every internet webpage they look at, so that if they are perhaps deleting messages from their email/myspace inbox, you can look at the stored screenshots and read the deleted messages when normally you never could! This is the tool I used to catch my girlfriend and it worked absolutely great. I really believe it’s the ultimate spying tool (and i’ve tryed a lot of things). Their Testimonials page shows that they’ve been on the news and featured in several magazines, so you should feel pretty good that you’ll accomplish what you’re after when you buy it.
I’ve gotten word of a secret coupon code for 25% off SniperSpy and/or Acespy! That’s at least $20 off! Too bad I didn’t know about it when I bought SniperSpy, haha. At the second purchase page, enter the following code: RXS-SPY25
Ask them for it
Yeah, that wasn’t what you wanted to hear. Well, the truth is, an honest partner will let you have it if there is absolutely nothing going on. The reason you should ask is they might be forthcoming. If your partner refuses, it does not necessarily mean they are cheating, but it is a red flag and can indicate they are hiding something
Other
People can also think their account was hacked if they neglect to log out and someone uses the computer after them. So be sure to logout and not just close the window, especially if you’re at a library, internet cafe, or the like.
So guys, i have provided you with almost all methods used for hacking Myspace accounts passwords. If you have any query about hacking myspace account passwords, please let me know.
Enjoy HaCkInG….

10. MSN Messenger hacks/tricks : Send continuous MSN nudges


Here I have already written several articles about Orkut and Myspace Tricks  but today you will know a very special MSN Messenger trick to send continuous MSN nudges to your friend online. This msn messenger trick will send number of continuous nudges. For this msn messenger trick to work, you should have msn messenger plus installed. If you don’t have msn messenger plus installed, download msn messenger plus.
What make me this to write this article as I had many times experienced continuous nudges while on online msn messenger with my friend. You get continuous msn nudges and hardly can do anything on msn messenger while being nudged. When tried to do the same in return, you get message ” You may not send a nudge that often”. Then i searched net for this msn messenger hack/trick and now informing you about this msn messenger nudge trick.
The steps are as below:
1. Download and install NudgeToolsScript (double clicking the .plsc file)
2. You will get warning message. Just check “I accept responsibility of installing this script” and click import.
3. Now, in msn messenger type “/sendnudge 1000 100″ (without quotes) and hit enter. This will make 1000 nudges every 100 milliseconds for friend. To stop nudges type “/stopnudge”.
4. While sending nudges, even your msn messenger window will be nudged. To avoid this, go to Tools > Option > Messages and uncheck the “Allow me to send and receive nudges”.
That’s it. Now, i hope you can send nudges to your friend online on web msn messenger. This msn messenger hack/trick will help you in nudging your online friend on msn messenger.

9. Hack Rapidshare to Beat Time Restriction and Download Limit… best trick


As it is a well known fact Rapidshare is world’s biggest file storage/sharing network and one of the most trafficked websites on the web. But the most irritating factor with the Rapidshare is the time restriction and time limit, this is why most of us looking for a backdoor to just bypass these files restrictions. Though in my previous post also I have mentioned the possible collection of tools and tips and premium link generators etc.. now in this post I am posting some of the hinds to help you more efficiently use Rapidshare. Skipping waiting time and bypassing download limits are Rapidshare hacks that everybody should know. These tips have been retested and continue to work well today, that is May 2011.
Do you know how Rapidshare keep tracking of the who is accessing and how much data has been transferred from their server…. by the IP address of any particular PC. This is how Rapidshare traces the users IP address to limit each user to a certain amount of downloading per day. To get around this, you need to show the Rapidshare server a different IP address.
Now here are some method better to say well known tested methods to bypass these restrictions
1. Short-Out the JavaScript:
    1. Goto the page you want to download
    2. Select FREE button
    3. In the address bar put the following: javascript:alert(c=0)
    4. Click OK
    5. Click OK to the pop-up box
    6. Enter the captcha
    7. Download Your File
2. Request a new IP address from your ISP server.
    Here’s how to do it in windows:
    1. Click Start
    2. Click run
    3. In the run box type cmd.exe and click OK
    4. When the command prompt opens type the following. ENTER after each new line.
    ipconfig /flushdns
    ipconfig /release
    ipconfig /renew
    exit
    5. Erase your cookies in whatever browser you are using.
    6. Try the rapidshare download again. 
    Frequently you will be assigned a new IP address when this happens. Sometime you will, sometimes you will not. If you are on a fixed IP address, this method will not work. To be honest, I do not know how to do this in linux/unix/etc. If this works for you, you may want to save the above commands into a batch file, and just run it when you need it.
3. Use a proxy with SwitchProxy and Firefox:
4. Use an anonymous service:
    Running your system through the tor network should in theory work; however, it is difficult to use and setup. Plus, you allow others to run their evil deeds through your system as well by using this system. Anonymizer 2005 is inexpensive, easy to use, but not free. Other pay services would likely work as well.
5. You can use a bookmarklet to stop your wait times:
    1. Open IE
    2. Right Click On This Link
    3. Select Add to Favorites
    4. Select Yes to the warning that the bookmark may be unsafe.
    5. Name it “RapidShare No Wait”
    6. Click on the Links folder (if you want to display it in your IE toolbar)
    7. Click OK
    8. You may need to close and reopen IE to see it
    9. Goto rapidshare and click the bookmarklet when you are forced to wait
This is all for now if it look s that I have missed something then why not just let me know… plz do post your valuable tricks or comments… it will benefit both the blog and blog readers..

8. List of most used tool to Hack Login Accounts from several Websites


The word Hacking has gone in such a mad way that everyone would like to try out their hands on how the most of the hackers claims to have hacked any website or login accounts. But most of them fails to do the same as they don’t have the right software. Today in this post i have found several software which hackers were using from a very long time and fortunately all of them are from Rapidshare. If you wanted to try them out any one of them just go through the link provided and use them at your own risk this blog will not be held responsible in any ways.
————————————————————————————–
AccessDiver_4.402
http://rapidshare.com/files/73578278/ad4…r.rar.html
Logins: pop-up
Basic tool. check http://accessdiver.com/ for updates and info!
————————————————————————————–
CForce
http://rapidshare.com/files/73575691/CFV1.01b.zip.html
Logins: pop-up, Form, Strongbox
A very simple and useful tool. Many start with this one.
————————————————————————————–
Sentry_1.4
http://rapidshare.com/files/73574138/sentry1.4.rar.html
Logins: Mainly pop-up
A very good tool
————————————————————————————–
HTTPBugger_v2.2
http://rapidshare.com/files/73577305/Htt…2.rar.html
Logins: Form/OCR
A tool for advanced people. even sites like pixandvideo or
peternorth are crackable with this little tool.
————————————————————————————–
Charon_0.6
http://rapidshare.com/files/73578915/Cha…6.rar.html
Proxy-checker!
[HIGHLIGHT="red"]Anonymity is most important.[/highlight]
Check your proxies with charon! Highly recommended.
————————————————————————————–
STAPH_1.25
http://rapidshare.com/files/73580097/StA…p.rar.html
Combo-leecher
Leech combos for themed combolists with STAPH!
————————————————————————————–
Raptor_3
http://rapidshare.com/files/73579738/Raptor.rar.html
Wordlister!
Build your own wordlists with Raptor!
—————————————————————————————-

So just go through with this whole list and enjoy whatever you wanted to do

6. What are session cookies? How they used to hack email accounts?

Once again welcome back a very interesting article about Session Cookies, which many hackers claiming to have used to hack email accounts or password of several other websites. In this tutorial you will learn how to hack yahoo account using session cookies.
Before we start any further let all you know what these session cookies are… sometimes which called Magic Cookie or Session ID?
However, if we try go in deep, there can be written whole article about these session id’s but in simple ways… these are the string stored when we tends to login our account. But with unfortunate with hackers luck these strings have very short span of life i.e. gets automatically deleted after a set period of time. Now the question where these strings are stored -  In any situation there are only two places where these keys gets stored first one is itself the server and the second one is the browser cookies. And the destruction takes place at three ways first is when you close your web browser, second is when you sign out of your account and third is if you left your account open for more than 20 minutes idle.
How this Cookies accessed on Local System?
As in this article we are using Yahoo account, so to get understand what this cookie is first you need to open yahoo.com and login to your account. After that you have login to yo ur account copy the below code written in bold and then paste in browser address bar.
javascript:alert(document.cookie);
This will open a popup box with a text something like this which is just not able to understand but we even not need to do so.. as only we need this code only.

How to hack email account using session cookies
Now create one fake account on yahoo.com and login in that account and retrieve the cookie in same manner and notice the changes in session ID’s.
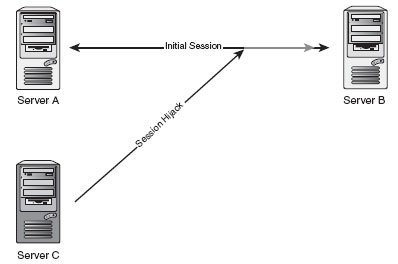
Now come to the main point hacking using the session ids…. For hacking the session cookies we first need the session cookies of the victim and its quite simple to get the session cookies of the victim. You just need to send him one link as soon as he clicks on that we will get his session cookie.
Here you should note this point as we have already mentioned that session hacking removes the authentication on the server as we have the AUTO LOGIN cookie. In this type of attack when victim sign out , then hacker will also sign out. But in case of YAHOO its little bit different, when victim signout but attacker still have the access to his account. Yahoo maintains the session for 24 hours and then destroy the session ID’s from its server.
Now how to step further to steal Session Cookies … follow the steps behind…
1. Go to the Website and register there:
2. Download the Cookie stealer files:
3. Now upload the four files on the website and create one empty directory naming Cookies as shown below:
4. Send the link of yahoo.php to victim. Now what will happen when user clicks on the yahoo.php is that its cookies are get stored into directory Cookies and simultaneously he is redirected to his account.
5. Now open the link Hacked.PHP to access the cookies. In my files the password is “password”. You need to put that to access the files.
6. You must have got the username of victim’s account. Simply Click on it and it would take you to inbox of victim’s yahoo account without asking for any password.
Now it doesn’t matter if victim signs out from his account, you would remain logged into it. 
Note: You can try this attack by using two browsers. Sign into yahoo account in one browser and run the code. Then sign in through other browser using stolen session.